Showing posts with label Misc. Show all posts

Tuesday, September 22, 2020

Misc: New blog

 I've been doing this for a while and the reason for "hiding" behind "nzpcmad" longer exists.

So jump over here for my new blog!

Thanks for all the comments and input over the years!

 I will still monitor the blog for comments etc.

Enjoy!


Tuesday, March 31, 2020

Misc : One million hits

I don't blog much here anymore but just hit a milestone:


Over a million hits!!!

Somewhat humbled to think I've helped a large percentage of those.

Enjoy!

Tuesday, September 11, 2018

Misc - a busy day at the office!


Busy on the forums!

Enjoy!

Friday, August 24, 2018

Misc : My audience

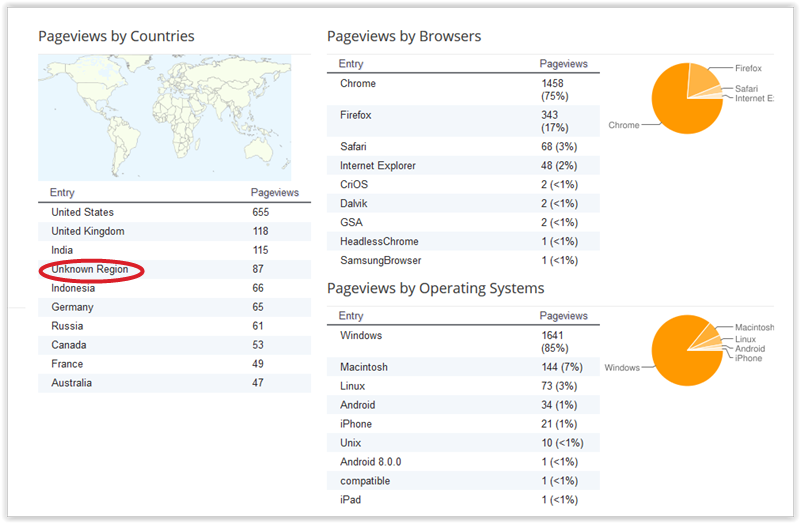
Just out of interest, my audience as reported by Blogger.


Strange that Google has "Unknown Region"?

Chrome is way ahead on the browsers and Windows is way ahead on the OS.

Would have thought the iPad figure would be higher but maybe iPad users have no interest in Identity :-)

Enjoy!

Friday, May 26, 2017

Misc : Top search result in Google

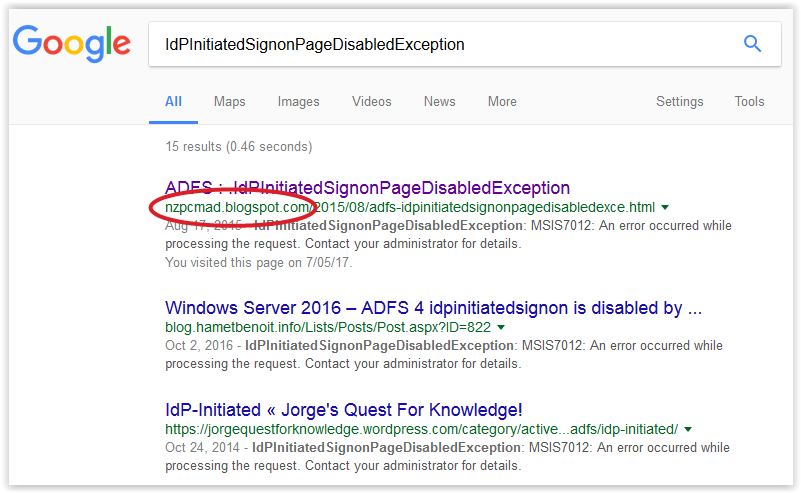
Now this I like :-)


Top search result - awesome.

Enjoy!

Wednesday, August 31, 2016

Misc : Microsoft Open Specifications

Microsoft publishes a list of open specifications that enable inter-operability over here.

These include a number of specifications that describe ADFS and WAP (Web Application Proxy).

These include:
The MS-ADFSPIP document describes the interface between ADFS and WAP.

There are tons of questions on the forum around "Do I have to use WAP as the proxy. Can I use any reverse proxy or a load balancer or F5 or Netscaler etc. ?"

You can as long as the proxy you want to use implements the standards.

Good luck with getting your vendor to confirm that they do and to demonstrate this fact.

In addition, your vendor may also need to comply with the rules around

[MS-OFBA]: Office Forms Based Authentication Protocol

if e.g. the request is 
  • from a Microsoft Office application that relies on the Office Forms Based Authentication (OFBA) Protocol
  • from non-Microsoft-Office clients accessing services that implement the OFBA protocol [MS-OFBA] that rely on ADFS for authentication
It also needs to ensure that the correct claims are set e.g.

http://schemas.microsoft.com/ws/2012/01/insidecorporatenetwork

which is "True" is accessing ADFS directly or "False" if accessing via WAP.

My advice : Just use the WAP - much less stressful - :-).

Enjoy! 

Friday, August 26, 2016

Misc : Creating self-signed certificates

I normally recommend SelfSSL7 but I was looking at Let's Encrypt which generates free CA SSL certificates.

This is in the context of Windows, specifically IIS SSL or securing ADFS.

To do this you need a client and one of the browser clients on the list was ZeroSSL.

If you click the Tools button, you'll see a "Self-Signed Certificate Generator".


There's a private key and a certificate.

Save the two files somewhere. If you save the certificate as a .cer file, you can double click on it and get the certificate wizard. You'll note that it has no private key which makes it useless for SSL. The certificate is valid for a year.

Now use OpenSSL to run:

openssl pkcs12 -export -out c:\xxx\adfs.pfx -inkey c:\xxx\zerossl.prv -in c:\xxx\zerossl.cer
Loading 'screen' into random state - done
Enter Export Password:
Verifying - Enter Export Password:

You'll need to pick a password.

Now if you double click on the .pfx file, the Import wizard will guide you as to installing it into the certificate store. You'll need to type in the password.

If you look at the "Enhanced Key Usage", you'll see it covers a lot of cases which is cool.


Enjoy!

Monday, May 16, 2016

Misc : "Why I Haven’t Fixed Your Issue Yet"

This really resonated with me.

Why I Haven’t Fixed Your Issue Yet

I don't do that much open source work - a bit - but nowhere near as much as I help out on Forums.

I help out on forums because I like to pay something back but it's not my full-time job and I don't get paid for it :-)

I get that you have a critical deadline, that your boss is on your back, that you are close to panic etc. but you are not the only one in the forums and like the writer above, I have to prioritise.

I give preference to those people who have actually tried to solve the problem e.g. they paste the ADFS claims rules that don't work.

People who write "HELP NEEDED" or "CRITICAL" and then leave a description like "Doesn't work" and I need three "answers" to tease out what version they are using against what repository and essentially expect me to do their job for them tend to be at the bottom.

And answers like "Don't have time to understand regex" pretty much guarantee that they will be back next week with another variation of the same problem.

Yes - it's hard but is it not part of your job to understand this stuff?

There are no excuses - there are hundreds of articles, books, Pluralsight etc.
'
Have a read of Jon Skeet's classic Writing the perfect question.

Help me to help you by describing and documenting the problem.

Oh and by the way, it's considered good etiquette to mark the question as answered, give reputation points or whatever if I help solve the problem.

Enjoy!

Wednesday, April 20, 2016

Misc : Switching over to https

Now that Blogger supports https, I've enabled https support for this blog.

I can't see any obvious errors.

If you find something, please leave a comment.

Thanks.

Enjoy!

Friday, December 04, 2015

Misc : 500 posts milestone

Well there you are folks - 500 posts!!!

The first post was in March 2005 and they have been accumulating steadily since then.

According to the Blogger widget, these are the most popular posts:


but this differs slightly from the Blogger stats.


As you can see from the Labels, I've covered a vast area but I blog mainly in the Identity sphere these days.

The ADFS label is by far the most prolific with over 100 posts to date.

Here's to the next 500.

Enjoy!

Wednesday, November 25, 2015

Misc : Certification for blogs

There's more and more stuff on the Internet - which includes more and more blogs - and the advice and information in a pile of them is rubbish.

It takes ages to sift through all the information discarding all the chaff until you find a few grains of wheat!

stackoverflow addressed this problem with questions. People who know what they are talking about get marked up and you can gauge the quality of the answer from the reputation of the answerer.

We need something like that for blogs.

So there would be some way of getting your blog "certified" e.g. the author has a stackoverflow rep. of more than 10,000 or whatever. Then you get a "badge" that you can display. And you can use this in a Google or Bing filter i.e. show me information from certified blogs only.

We can but dream!

Enjoy!

Thursday, October 01, 2015

Misc : Invest in yourself

aka "Make yourself more awesome".

I watched this presentation from Ignite NZ 2015:

Career Path Control

There were a number of things here that totally resonated with me.

And then I saw:

How to Be Awesome

OK - you don't have to be as "batshit insane" (watch the video) as this but it's an interesting approach.

And then I started to think about how I approached this.

First of all I started reading blogs. I use FeedDemon as a RSS reader and I currently have about 180 feeds - mainly in the Microsoft / Azure / Identity space.

I flick through them every morning and read the ones I find more interesting.

How do I find them? I'm doing something, run into a problem, Google and then I find a good answer on a blog and then I take a stroll around other articles in the blog. If it's stuff I may find useful, I add it to my feed. Essentially, people who write good blog posts tend to keep on doing this and I want to know about them.

Sadly, I find in interviews that very few people do this. But it's the main reason:
  • I know more than most people around here
  • I'm more informed
  • I'm the one who gets the news first and then tells other people
All of these do wonders for your reputation.

The other thing I do is to be active on Forums.

I'm in the top 2% on stackoverflow and I also help out on some of the MSDN forums.

The first time I attempted to answer a question on stackoverflow I just about wet myself. I imagined a deluge of criticism but actually all I got was two up votes. So then I started answering more and more and my reputation grew and grew. I try and answer at least one question a day. Basically, I have made my own little niche and recently got my adfs badge.

There's a Chinese saying "A journey of a thousand miles starts with the first step".

People ask "How do I get into stackoverflow? All the questions have been answered by people way smarter than me?".

My advice is always the same - there's over 10 million questions there and most have answers. Find a good question where the answers pretty much suck and write a better one.

And keep doing that. And that will give you the confidence to be the one to answer a question first. Don't be despondent if it takes a while to get an up vote. You''l find that you mainly work in a small group of tags. Start checking those tags every day. Each tag has a RSS feed so I get all the new questions in FeedDemon. And then I answer them.

No - I don't know all the answers. Actually, I rarely know the complete answer. But I research the question. And by doing that, I learn more. So it becomes a self-fulfilling prophecy. And if I find something I think others will find useful, I expand it into a blog post on my blog.

Which is a nice segue into my next point. Start writing a blog. Blog about how you solved a problem. Blog about a cool presentation you watched. If there's a stackoverflow question that keeps occurring, write a really comprehensive blog post and then link it plus a summary in your stackoverflow answer.

You also need to cough up some hard cash, Buy some books or e-books around your particular area and read them. Get a Pluralsight subscription. Buy some tools e.g. ReSharper. I work in the Identity area so there's a lot of SAML-P (P for Protocol) and there's no Microsoft client side stack for this. So I bought one (ComponentSpace) just so I could research SAML, do some PoC, write some of these blog entries etc.

Basically, just do it!

So there you have a number of different approaches with the same outcome.

Choose the one that works for you and make yourself more awesome.

Enjoy!

Thursday, August 13, 2015

Misc : European law for cookies

Apparently, European law requires a notice that this site uses cookies.

"European Union (EU) laws require you to give EU visitors information about cookies used on your blog. In many cases, these laws also require you to obtain consent.

As a courtesy, we have added a notice on your blog to help meet these regulations."

So Google has added this feature to Blogger.

If you go to e.g. nzpcmad.blogspot,fr (for France), you see:


Very neat!

BTW: From reading Troy Hunt's blog, I found that he also uses Blogger :-).

Enjoy!

Friday, July 24, 2015

Misc : Just because something is there doesn't mean you have to use it.

I came across a situation recently that made me smile!

For various reasons, this company uses ADFS and IdentityServer 2.0.

They then had a requirement to secute a Web API.

Web API's require a JWT token and they knew that IdentityServer allows you to convert token types for RP i.e.


So the path is Web API --> IS --> ADFS and then return the SAML token and convert to JWT.

It works fine but if they had taken a step back and asked "What is the correct way to do this" and not been sidetracked by the JWT issue, then they would have found a much better solution which is also supported by IS viz. OAuth2.

As it transpired, they needed to authenticate against AD which IS doesn't do and ADFS 3.0 has limited OAuth functionality but when ADFS vNext on Server 2016 comes out, hopefully they will convert the above and use OAuth2!

Enjoy!

Monday, May 25, 2015

Misc : Citrix Receiver on Firefox

I do a lot of work for customers and to do that I need remote access to their servers.

The VPN tool of choice these days seems to be Citrix Receiver.

If you are experiencing problems with FireFox i.e. you can login and get the portal but when you click on one of the icons e.g. desktop or remote desktop and you see the little wheel spin for a few moments and then stop and then nothing happens, try this:

Tools / Options / Applications


Ensure that "Connection Manager" is selected and not "Receiver".

Enjoy!

Wednesday, September 24, 2014

Misc : Popular posts

There is a little widget that's supposed to do this but here are the actual statistics.


Notice the number of ADFS hits!

Enjoy!

Misc : GitHub for Windows - Clone in Desktop

GitHub for Windows is a neat tool but suffers from a severe lack of documentation.

I find a project I like, click "Clone in Desktop" on the RHS and it takes me to a screen saying "Download GitHub for Windows" even though I have the damn thing already installed.

So ^^%$$% frustrating.

Mr. Google to the rescue and after a number of false starts (Google sucks more and more at delivering useful search results) I discovered that you need to log-in first on the GitHub site.

Then all is OK.

Going by the number of hits I found on this, 99% of this would be avoided if GitHub put a notice to that effect on the page e.g.

"You must first Login".

Enjoy!

Wednesday, April 16, 2014

Misc : Zooming the ZoomIt window

ZoomIt is a fantastic tool for presentations. You'll find it at:

ZoomIt

But I've always battled to get it to display exactly where I want and tracking around the zoomed screen is a nightmare.

Then I figured out that before you hit "Ctrl / 1" to zoom, put the cursor at the middle of the section you want to zoom.

Then zoom.

You can make minor adjustments by moving the mouse, use the trackwheel to zoom in / out, click the left mouse button to "stabilise" and then you are in the "Ctrl / 2" window by default so "Ctrl / Shift" will draw an arrow etc.

And it would be remiss of me not to point out that you can do this in Windows via the built-in commands. In a browser, type "Windows key" and then "+" to zoom out and then  "Windows key" and then "-" to zoom back in. This is in fact the Magnifier tool.

Enjoy!

Friday, January 17, 2014

Misc : How much is my blog worth?

Came across this site:

Worth of Web Calculator

According to this, my blog is worth the princely sum of $69.00 !

Any offers :-)

Enjoy!

Monday, January 13, 2014

Misc : MSDN 2000 points!

Finally passed the 2000 point barrier on the MSDN forums!

It's much harder to get rep. on MSDN than on stackoverflow.

Enjoy!